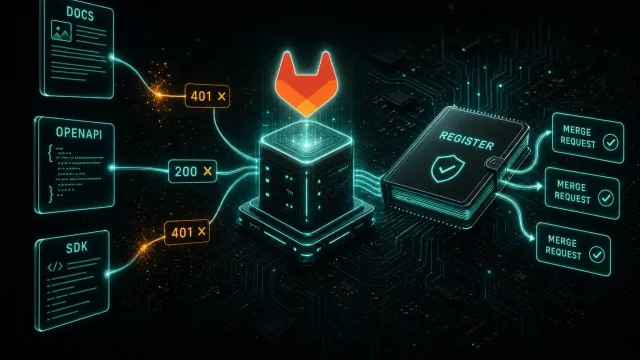
What building a GitLab MCP server taught me about GitLab's API
Building and checking an MCP server against GitLab found a 401 that meant 403 and writes answered as successes that saved nothing; each went upstream.
Notes
2 posts about this topic
Building and checking an MCP server against GitLab found a 401 that meant 403 and writes answered as successes that saved nothing; each went upstream.
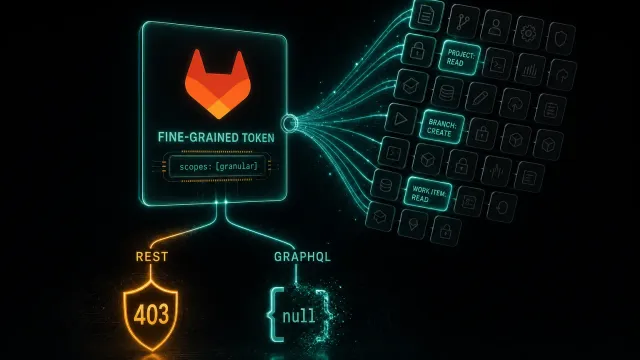
A GitLab fine-grained token holds a grant, not scopes: REST refuses outside it, GraphQL answers null. I derive what each API action needs, ahead of time.
No posts match your filters.